
What Is SAP Cyber Security?
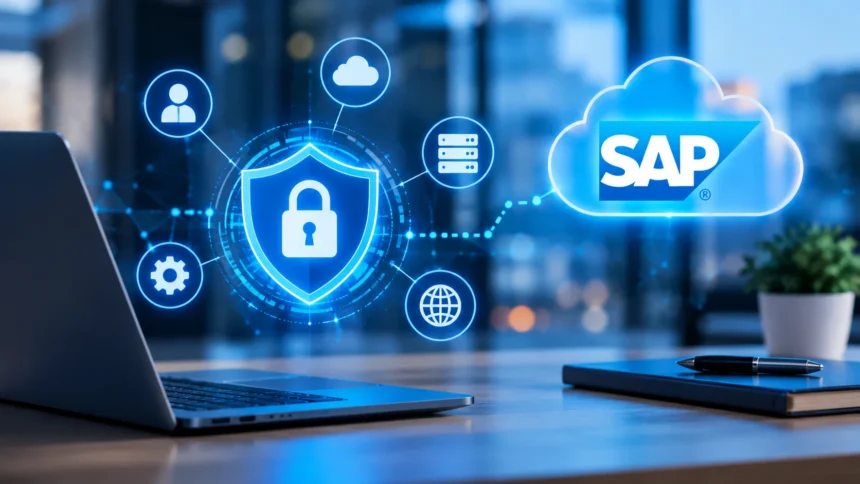
SAP cyber security is the practice of protecting SAP systems, applications, users, business processes, and sensitive information from unauthorized access, misuse, disruption, and cyber threats. It combines security controls, identity management, secure configuration, monitoring, data protection, vulnerability management, and incident response to keep an SAP environment dependable and protected.
SAP platforms often sit at the center of important business activities, including finance, procurement, human resources, manufacturing, supply chain management, and customer operations. Because these systems handle valuable business information, a security weakness can affect far more than an individual application. SAP security therefore focuses on protecting both technology and the business processes connected to it.
A strong SAP cybersecurity strategy considers the entire SAP landscape rather than treating security as a single technical setting. This can include SAP S/4HANA, SAP ERP, SAP Business Technology Platform, interfaces, databases, cloud environments, custom applications, and connected systems. The goal is to reduce security exposure while allowing authorized employees and applications to perform legitimate business activities.
Why Is SAP Cyber Security Important?
SAP environments contain information that can be highly sensitive, such as financial records, employee information, supplier details, customer data, pricing information, intellectual property, and operational records. Unauthorized access to this information can lead to financial loss, privacy problems, operational disruption, and reputational damage. Security controls help reduce the possibility and impact of these incidents.
Another reason SAP security matters is the complexity of modern enterprise environments. An SAP system rarely operates alone, because it may connect with identity platforms, databases, web applications, third-party services, mobile applications, APIs, and external partners. Each connection can introduce additional security considerations that need careful management.
Cybersecurity also supports business continuity. If an attacker compromises an important SAP environment, essential processes such as purchasing, payroll, accounting, inventory management, or production planning may be interrupted. Effective SAP security helps organizations maintain control over access, detect suspicious activity, protect critical information, and recover more confidently when security incidents occur.
What Are the Main Components of SAP Cyber Security?
SAP cybersecurity consists of several connected security disciplines. These include identity and access management, authentication, authorization, data protection, secure communications, system hardening, vulnerability management, security monitoring, application security, and incident response. Each area addresses a different part of the risk surrounding an SAP environment.
Identity and access management determines who can enter an SAP environment and what actions each person or technical account can perform. Authorization controls are especially important because an authenticated user should not automatically have access to every business function. Strong role design helps ensure that permissions match actual job responsibilities.
Technical protection is equally important. Secure configuration, encryption, network segmentation, patch management, logging, vulnerability assessment, and secure interfaces can reduce common attack paths. Security teams also need visibility into unusual behavior so that suspicious activity can be investigated before it becomes a larger business problem.
How Does SAP Identity and Access Management Work?
Identity and access management, often called IAM, is a central part of SAP security. It covers user identities, authentication methods, authorization roles, access policies, and account lifecycle management. The objective is simple: the right person should have the right access for the right business purpose, without unnecessary privileges.
SAP authorization concepts can become complex because enterprise users often need access to multiple transactions, applications, reports, and business processes. Excessive permissions can increase risk, while poorly designed roles can interfere with legitimate work. Security teams therefore need to review roles carefully and apply the principle of least privilege.
Authentication adds another layer of protection by verifying that a person or system is genuinely who it claims to be. Strong passwords, multifactor authentication, single sign-on, identity federation, and controlled service accounts can strengthen access security. Regular access reviews are also important because employees change departments, responsibilities change, and accounts can remain active longer than necessary.
How Does SAP Protect Business Data?
Data security in SAP focuses on keeping information confidential, accurate, and available to authorized users. Important controls can include encryption, access restrictions, secure database configuration, protected backups, retention policies, and careful handling of sensitive information. These measures help reduce the chance that valuable business data is exposed or altered without authorization.
Data can face different risks depending on where it exists and how it moves. Information stored inside an SAP database requires different safeguards from information transferred through an API, integration platform, web connection, or external application. Secure communication protocols and appropriate access controls help protect information while it travels between systems.
Data security also involves understanding which information is most sensitive. Financial records, personal information, authentication details, intellectual property, and strategic business data may require stronger controls than routine operational information. Classification, monitoring, access governance, and secure retention practices can help organizations manage information according to its business and security importance.
What Are Common SAP Cybersecurity Threats?
SAP systems can face threats such as stolen credentials, excessive privileges, unpatched vulnerabilities, insecure configurations, malicious insiders, compromised integrations, and application-level attacks. Attackers may target an SAP environment directly or compromise another connected system before attempting to reach SAP resources. This makes the broader technology environment relevant to SAP security.
Misconfiguration is another significant concern. Weak passwords, unnecessary permissions, exposed services, outdated components, poorly protected interfaces, and excessive administrative access can increase an organization’s attack surface. Even when the underlying SAP software is functioning correctly, insecure settings can leave important business processes exposed.
Custom development can introduce additional risks. Organizations frequently extend SAP environments with custom code, integrations, APIs, workflows, and external applications. Security weaknesses in these extensions can become pathways into sensitive business functions, making secure development practices, code review, vulnerability testing, and careful interface management important parts of SAP cybersecurity.
How Does SAP Security Monitoring Work?
Security monitoring helps organizations identify unusual events and investigate activity that may indicate an attack. Logs can contain information about authentication attempts, permission changes, administrative actions, configuration changes, application events, and other security-relevant activity. Reviewing this information can help security teams recognize patterns that might otherwise remain unnoticed.
Threat detection becomes more effective when security events are analyzed in context. For example, an unusual login may not mean much on its own, but an unusual login followed by privilege changes and access to sensitive financial data may deserve immediate investigation. Correlating events across SAP and connected systems can help analysts understand what is actually happening.
Incident response is the next important step when suspicious activity is confirmed. Security teams may need to contain affected accounts or systems, investigate the source, preserve evidence, correct weaknesses, and restore normal operations. A documented response process helps reduce confusion during an incident and supports faster, more controlled decision-making.
What Is SAP Cloud Security?
SAP cloud security focuses on protecting SAP applications and data running in cloud environments. It includes identity management, access control, encryption, secure configuration, application security, monitoring, vulnerability management, tenant protection, and resilience. Cloud environments can change quickly, so security controls need continuous attention rather than occasional review.
Cloud security also involves shared responsibilities. Depending on the service and deployment model, SAP, the customer, and the underlying cloud infrastructure organization may each handle different security responsibilities. Customers still need to manage areas such as user access, application configuration, data access, and security-related settings that fall within their control.
Moving SAP workloads to the cloud does not remove cybersecurity responsibilities. Instead, it changes how some controls are implemented and who manages them. Organizations should understand their cloud architecture, identify responsibility boundaries, secure identities and configurations, monitor activity, and regularly assess whether their security controls match the risks of their current environment.
How Does SAP Cyber Security Support Compliance?
SAP cybersecurity can support organizations that must meet privacy, security, financial, industry, or internal governance requirements. Compliance commonly involves access controls, audit trails, segregation of duties, data protection, change management, vulnerability management, and documented security processes. The exact requirements depend on the organization, industry, location, and type of information handled.
Segregation of duties is particularly important in business systems. It helps prevent one individual from controlling incompatible activities, such as initiating a transaction and approving the same transaction. Proper role design, access reviews, approval workflows, and audit monitoring can help identify conflicts before they become significant control weaknesses.
Auditability is another important part of SAP security governance. Organizations need reliable records that show who accessed systems, what changes occurred, and when important actions took place. Clear security policies combined with appropriate logging and periodic reviews can make investigations and compliance assessments more manageable.
How Can Businesses Improve SAP Cyber Security?
A practical SAP security program begins with visibility. Organizations should understand their SAP architecture, connected applications, interfaces, users, privileged accounts, custom developments, and sensitive data. Without a clear understanding of the environment, security teams can struggle to identify which systems and access paths require the greatest attention.
Next, organizations should strengthen foundational controls. These can include least-privilege access, multifactor authentication, secure configuration, timely security updates, protected interfaces, network controls, encryption, backup protection, and continuous monitoring. Security testing should also examine custom applications and integrations because weaknesses can exist outside the SAP core.
Finally, SAP security should be treated as an ongoing business discipline rather than a one-time technical project. User permissions need periodic review, vulnerabilities need timely attention, logs need monitoring, and incident procedures need testing. Regular security assessments help organizations adapt as business processes, technology architectures, regulations, and cyber threats change.
What Skills Are Needed for SAP Cyber Security?
SAP cybersecurity requires a mixture of SAP knowledge and broader information security skills. Professionals may work with SAP authorization concepts, identity management, secure configuration, vulnerability management, network security, application security, monitoring, and incident response. Understanding how business processes operate inside SAP is also valuable because security decisions can affect everyday operations.
Technical skills can vary according to the role. An SAP security administrator may focus heavily on roles, authorizations, users, authentication, and system configuration, while a security analyst may concentrate more on monitoring, threat detection, investigation, and response. Application security specialists may work with secure coding, custom developments, interfaces, APIs, and vulnerability testing.
Strong communication and analytical thinking are also important. SAP security professionals often work with system administrators, developers, auditors, business owners, compliance teams, and senior management. The ability to explain technical risks in practical business terms can help organizations make better decisions about access, security controls, investment priorities, and operational risk.
What Is the Future of SAP Cyber Security?
SAP environments are becoming increasingly connected through cloud services, APIs, mobile applications, automation, analytics, and integrated business platforms. This expanding connectivity can improve efficiency while also increasing the number of systems and identities that security teams must protect. Modern SAP cybersecurity therefore requires broader visibility across applications, infrastructure, users, data, and integrations.
Identity security is likely to remain a major focus because unauthorized access can quickly turn into business risk. Strong authentication, adaptive access controls, privileged access management, automated access reviews, and improved identity governance can help organizations maintain tighter control. Security teams will also need better ways to detect unusual behavior across complex enterprise environments.
Another important direction is greater emphasis on resilience. Preventing every security incident is difficult, so organizations also need strong detection, response, recovery, and continuity capabilities. A mature SAP cybersecurity strategy combines preventive controls with monitoring and response so that businesses can limit disruption and restore important operations more effectively.
Conclusion
SAP cybersecurity is the discipline of protecting SAP applications, data, identities, integrations, infrastructure, and business processes from cyber threats and unauthorized activity. It combines access management, secure configuration, data protection, vulnerability management, monitoring, incident response, and governance. The strongest approach considers the entire SAP landscape rather than focusing on one security setting.
For organizations, SAP security is closely connected to business continuity and operational trust. A compromised account, exposed interface, weak authorization, or vulnerable component can affect important financial and operational activities. Strong controls, regular reviews, security monitoring, and clear responsibility boundaries can significantly improve the overall security posture.
As SAP environments continue to evolve across cloud and connected enterprise technologies, cybersecurity needs to remain an ongoing priority. Businesses that understand their risks, protect sensitive information, control access, monitor activity, and prepare for incidents can build a more resilient SAP environment without making security unnecessarily difficult for legitimate users.
FAQs About SAP Cyber Security
What is SAP cyber security in simple terms?
SAP cyber security means protecting SAP systems, applications, business data, users, and connected technologies from unauthorized access, attacks, misuse, and disruption. It combines access controls, secure configuration, monitoring, data protection, and incident response.
Why is SAP security important for businesses?
SAP often supports critical processes such as finance, purchasing, human resources, manufacturing, and supply chain operations. Strong security helps protect sensitive information, reduce unauthorized access, support continuity, and limit the impact of cyber incidents.
What does an SAP security professional do?
An SAP security professional may manage users, roles, authorizations, authentication, security configuration, access reviews, monitoring, and vulnerability management. The exact responsibilities depend on whether the role focuses on administration, governance, application security, or threat detection.
What are common SAP security risks?
Common risks include excessive user permissions, stolen credentials, weak configurations, outdated components, insecure interfaces, vulnerable custom code, compromised accounts, and poor monitoring. Connected systems can also introduce additional pathways into an SAP environment.
How can a company improve SAP cybersecurity?
A company can strengthen SAP cybersecurity by applying least-privilege access, multifactor authentication, secure configurations, timely security updates, protected communications, strong monitoring, regular access reviews, vulnerability assessments, and tested incident-response procedures.