
What Is a Password Hash in Cybersecurity?
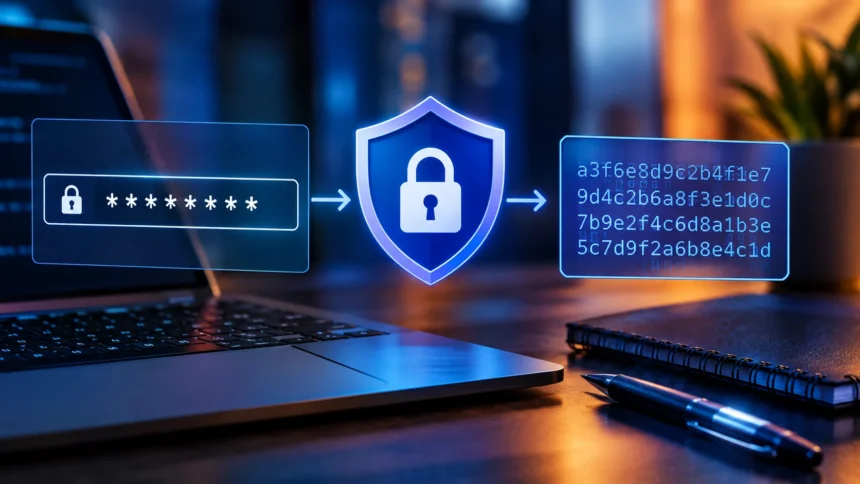
A password hash is a transformed version of a password that is designed to protect the original secret. Instead of storing a user’s actual password, a system stores the output of a password hashing function. When the user signs in, the entered password is processed again and compared with the stored hash.
Password hashing is a core part of cybersecurity because stolen password databases can expose thousands or millions of accounts. A properly designed password storage system makes those stolen values much harder to turn back into usable passwords. Hashing therefore adds an important layer of protection against credential theft, database breaches, and unauthorized account access.
It is important to understand that password hashing is different from encryption. Encryption is designed so authorized users can recover the original information with a key, while password hashing is designed to be one-way. A secure password hash should make it computationally difficult to determine the original password from its stored value.
How Does Password Hashing Work?
When someone enters a password during account registration, the application sends that password through a password hashing algorithm. The algorithm converts the password into a fixed-format value known as a hash. The application then stores the hash rather than keeping the original password in readable form.
During a later login attempt, the entered password passes through the same password-hashing process. The resulting value is checked against the stored password hash associated with the account. If the values match according to the system’s verification method, the password is considered correct and access can continue.
Modern password storage normally uses additional safeguards, especially a unique salt for every password. A salt is random data combined with the password before hashing, making identical passwords produce different stored hashes. This helps reduce the effectiveness of precomputed attacks and makes large-scale password cracking considerably more difficult.
Why Are Password Hashes Important in Cybersecurity?
Password hashes matter because passwords are among the most targeted forms of digital authentication. If a database stores passwords in plain text, anyone who gains unauthorized access to that database may immediately see the credentials. Hashing reduces this exposure by keeping the stored representation different from the original password.
A data breach can still be serious even when passwords are hashed. Attackers may attempt offline password cracking by repeatedly guessing common passwords and comparing the resulting hashes with stolen values. Strong password hashing algorithms are deliberately designed to make these repeated guesses slower and more expensive.
Password hashing also supports better security practices across websites, applications, and enterprise systems. When combined with strong passwords, unique salts, multi-factor authentication, account protection, and secure access controls, it can significantly reduce the impact of stolen credential databases. It is therefore an important component of secure authentication architecture.
Password Hashing vs. Password Encryption
Password hashing and encryption solve different security problems. Hashing transforms information into a one-way representation, while encryption transforms information so it can later be recovered with the appropriate key. Passwords generally do not need to be recovered, so secure systems normally hash them instead of encrypting them for storage.
Encryption is useful when an application must retrieve the original data later. For example, sensitive information that needs to be read by an authorized system may require encryption and controlled key management. Password verification works differently because the system only needs to determine whether the submitted password matches the stored authentication value.
Confusing hashing with encryption can lead to weak password storage decisions. Storing passwords with reversible encryption means someone who obtains both the encrypted database and the required key could potentially recover the original credentials. A properly selected password hashing approach reduces this risk by avoiding the need to retain recoverable passwords.
What Is a Salt in Password Hashing?
A salt is a random value added to a password before the password passes through a hashing function. Each account should have its own unique salt, even when several people happen to choose the same password. The salt is normally stored alongside the resulting password hash because it does not need to remain secret.
Without unique salts, identical passwords can generate identical hashes when the same hashing method is used. An attacker who sees repeated values could quickly recognize that multiple accounts share a password. Unique salts prevent this direct comparison and make large-scale password cracking more difficult.
Salting also weakens the usefulness of precomputed password databases, sometimes called rainbow tables. An attacker must account for the individual salt when testing password guesses, rather than relying on one precomputed value for every account. Salted password hashing is therefore a standard security practice for protecting stored credentials.
Which Algorithms Are Used for Password Hashing?
Not every hashing algorithm is suitable for password storage. General-purpose functions such as SHA-256 and SHA-512 are designed to perform calculations quickly, which is useful in many security applications but undesirable for password protection. Fast hashing can allow attackers to test enormous numbers of guesses in a short period.
Password-specific algorithms are intentionally slower and configurable. Argon2, bcrypt, scrypt, and PBKDF2 are widely recognized approaches for password hashing, with each using different techniques and configuration options. Their parameters can be adjusted so password verification requires meaningful computational resources.
Argon2 is particularly notable for its memory-hard design, which makes certain large-scale cracking strategies more demanding. bcrypt has been widely used for many years and includes a configurable work factor. PBKDF2 remains common in systems that require an established password-based key derivation approach, while scrypt also uses significant memory to increase cracking difficulty.
What Happens When a Password Hash Is Stolen?
A stolen password hash does not automatically reveal the original password. However, it can become valuable to an attacker who performs offline password guessing against the stolen data. The attacker may test likely passwords, pass those guesses through the relevant hashing process, and compare the results with the compromised hashes.
Weak passwords are especially vulnerable because attackers can prioritize common words, predictable patterns, previously exposed credentials, and short combinations. Even a strong hashing algorithm cannot compensate fully for a password that is easy to guess. Password length, uniqueness, and resistance to common guessing patterns remain important.
The security impact also depends on the hashing method, salt usage, configuration, and quality of the password itself. A modern, properly configured password hashing function can make large-scale guessing substantially more difficult. Still, organizations should treat a stolen credential database as a serious security incident and respond accordingly.
Why Fast Hashing Is Not Always Better for Passwords
In many areas of computing, speed is desirable because systems need to process information efficiently. Password storage has a different requirement because an attacker can repeat password guesses millions or billions of times. A password hashing function that takes slightly longer can therefore make automated guessing much more expensive.
Password-specific hashing algorithms use configurable work factors, memory requirements, or iteration counts to control how demanding each verification becomes. These settings can be tuned according to the capabilities of the application and its infrastructure. The objective is to make legitimate authentication practical while increasing the cost of repeated offline guesses.
This does not mean password verification should become unnecessarily slow. Excessive computational requirements can affect users and place unnecessary pressure on servers. Good password security balances usability with resistance to password cracking, while allowing parameters to be reviewed and strengthened as computing hardware becomes more capable.
Common Password Hashing Mistakes
One common mistake is storing passwords in plain text. Another is using a general-purpose fast hash without an appropriate password-specific design. These approaches can leave credentials much more exposed if attackers gain access to an authentication database.
Reusing the same salt across many passwords is another weakness because it reduces the protection gained from individual salts. Hard-coded salts are also unsuitable because they are predictable rather than unique. A secure implementation should rely on a reputable password-hashing library that handles salt generation and verification correctly.
Another problem is using outdated algorithms or weak configuration settings for too long. Security standards and computing capabilities change over time, so password storage systems need periodic review. Organizations should also support password resets, multi-factor authentication, breach response procedures, and other controls that reduce dependence on passwords alone.
How Strong Passwords Work With Hashing
Password hashing protects stored credentials, but it does not make weak passwords strong. If someone chooses a short and predictable password, an attacker may still guess it through automated password cracking. Strong hashing increases the effort required for each guess, while a strong password increases the number of guesses an attacker may need.
A long, unique password or passphrase is generally more resistant to guessing than a short password with minor substitutions. Reusing one password across several services also increases risk because a breach at one service can expose credentials used elsewhere. Password managers can help people maintain unique credentials without relying on memory for every account.
Multi-factor authentication adds another layer because a password alone is no longer sufficient for access. Depending on the system, the additional factor may involve a security key, authenticator application, or another approved verification method. Combining strong passwords, secure hashing, unique salts, and additional authentication controls creates a stronger overall security posture.
How Organizations Can Improve Password Hash Security
Organizations should begin by using a modern, dedicated password-hashing algorithm with appropriate parameters. Passwords should never be stored in readable form, and each password should receive a unique cryptographic salt. Password verification should also happen through trusted security libraries rather than improvised hashing code.
Security teams should regularly review password storage settings and monitor developments in password-cracking hardware and defensive standards. When older hashing methods are encountered, migration can often happen gradually by rehashing credentials after successful authentication. This allows security improvements without requiring every user to change a password immediately.
A strong password policy should work alongside secure storage rather than replacing it. Organizations can also use multi-factor authentication, login monitoring, breached-password detection, rate limiting, session protection, and secure account recovery procedures. Together, these controls reduce the chances that a stolen password or compromised hash will become an easy path into an account.
Password Hashing and the Future of Account Security
Password hashing will remain relevant because passwords continue to appear across websites, business applications, operating systems, and online services. However, authentication is increasingly moving toward methods that reduce dependence on passwords. Passkeys, hardware security keys, and other phishing-resistant technologies can reduce some of the weaknesses associated with traditional credentials.
Even as newer authentication methods become more common, existing systems still contain large amounts of password-based infrastructure. Those systems need secure credential storage for as long as passwords remain part of their authentication process. Strong password hashing therefore remains an important defensive measure rather than a technology that can simply be ignored.
The broader lesson is that password security depends on multiple layers rather than one technique. Hashing protects stored password representations, salts make identical passwords harder to correlate, strong credentials resist guessing, and additional authentication factors reduce the consequences of password compromise. Together, these practices form a more resilient approach to identity and access security.
Conclusion
A password hash is a one-way representation of a password used to protect credentials stored by an application or service. Instead of retaining the readable password, a secure system stores a hash and later verifies submitted passwords against that stored value. This approach helps limit the damage caused by unauthorized access to credential databases.
Strong password hashing depends on more than selecting a hashing algorithm. Unique salts, suitable work factors, secure implementation, strong passwords, and regular security reviews all matter. Algorithms designed specifically for password storage, such as Argon2, bcrypt, scrypt, and PBKDF2, are better suited to this purpose than fast general-purpose hashing functions.
Understanding password hashes helps explain how modern authentication systems protect user credentials against database theft and password cracking. For individuals and organizations alike, secure password storage should work alongside multi-factor authentication, unique credentials, careful account recovery, and broader cybersecurity controls.
Frequently Asked Questions
What is a password hash?
A password hash is a one-way transformed value generated from a password. Secure applications store this value instead of the readable password and use password verification to check future login attempts.
Can a password hash be decrypted?
A password hash is not encrypted data, so it is not normally decrypted. Attackers instead attempt guesses and compare their resulting hashes with the stolen value.
Is SHA-256 good for password storage?
SHA-256 is a secure cryptographic hash function, but it is designed to be fast. Password storage generally benefits from slower, password-specific algorithms such as Argon2, bcrypt, scrypt, or PBKDF2.
What does a salt do to a password hash?
A salt is unique random data combined with a password before hashing. It helps ensure that identical passwords have different stored hashes and makes precomputed password attacks much less useful.
What happens if password hashes are stolen?
Attackers can attempt offline password cracking by guessing passwords and comparing the resulting values with stolen hashes. Strong passwords, unique salts, and slow password-hashing algorithms can make this process substantially harder.